Key Takeaways
- Zoom’s popularity has made it a prime target for security breaches, but most threats can be prevented with simple settings adjustments. Taking a few minutes to configure your account correctly goes a long way.
- Never share meeting invite links through social media, even on private accounts. Only secure email servers provide adequate protection for meeting credentials.
- Features like the waiting room, meeting lock and restricted screen sharing give organizers strong control over who can access a meeting. Configuring these before each meeting significantly reduces security risks.
- Home internet connections now need the same security vigilance as corporate networks. Avoiding suspicious links, updating security software and checking in with your internet provider are all smart precautions.
- Keeping Zoom updated is one of the simplest ways to stay protected. Security patches are built into new releases and can be applied in just a few clicks.
Video conferencing services are being utilized by hundreds of thousands of companies across industries and around the world like never before. One of the most popular platforms, Zoom, has had its fair share of security breaches as it sees huge jumps in traffic in the time of COVID-19. While businesses, governments and schools use Zoom to continue their operations from remote locations, staying safe online is more important than ever.
To help companies and individuals protect themselves and their data, here are some video conferencing safety tips offered by Zoom and University of San Diego cybersecurity experts.
1. Don’t Make the Meeting Public
This might seem like a no-brainer, but leaving meetings public is a common oversight. There have been numerous reports of hacked Zoom meetings, otherwise known as Zoom bombing, which could often be avoided with a simple settings switch.
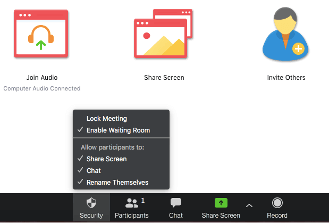
A security reinforcement that meeting organizers can use is the feature called “Lock Meeting.” This function allows the meeting organizer to lock out any new participants once the meeting starts. Even if a person has the invitation URL, locking the meeting prevents anyone from getting in.
2. Use Random Meeting IDs
Zoom meeting IDs are 10- or 11-digit numbers that are assigned to every individual meeting. While they are all random assortments of numbers, companies can run into security issues when they have recurring meetings that continually use the same ID numbers.
Even if meetings are daily or weekly occurrences with the same people, be sure to change the meeting ID and private meeting password frequently. This will protect the entire organization from unwanted visitors or security breaches.
3. Share Invite Links via Secure Communication
Only share meeting invites via secure email servers. Many people run into security issues when they invite participants to Zoom conferences via Facebook, Twitter or Instagram. These platforms, even if your profile is private, are not safe enough to prevent someone from getting your information. Even if you use programs like Facebook Messenger or direct message via Twitter or Instagram, that is still not secure enough.
4. Utilize the Waiting Room Feature
The waiting room feature allows the meeting organizer to control who enters the video conference, even if they have been invited. Every time an invitee tries to enter the meeting, the organizer will have to grant individual permission. The waiting room also allows organizers to take a roll call of who is and isn’t in attendance. This may seem cumbersome, but this is a critical tool to prevent unwanted visitors.
The waiting room option is located under the security tab on the video screen and can simply be toggled on and off for each meeting.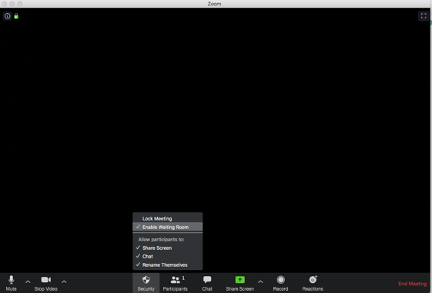
5. Only Allow Hosts to Control Screen Sharing
Screen sharing is an essential feature of any video conferencing service, as it allows all meeting participants to be on the same page, literally, when discussing a topic or project. The security issue can arise when the meeting organizer is not in control of the screen share, and an uninvited person starts sharing their screen or unsavory content.
To secure the screen sharing option but still allow invited meeting participants to share their screens, the meeting organizer must go into the advanced sharing options tab. Here, they can select how many participants can share, who is allowed to share, and most importantly, who can start sharing when someone else already is. This control should be left to the organizer who can serve as a proctor to what content gets shared in the meeting.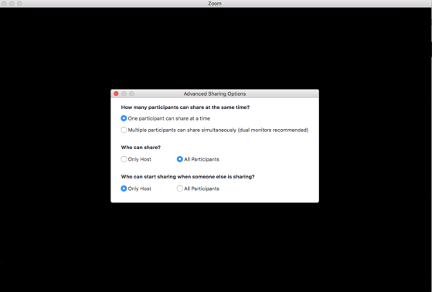
6. Make Sure Everyone’s Home Internet is Secure
Professional internet connections are usually more secure than private ones, but with everyone working from home, it’s more important than ever to ensure connection security. People can call their internet providers to learn more about securing their home internet and can also take extra steps to ensure that nothing malicious compromises the system.
During this time of work from home, people should treat their home internet connection like they do their corporate or work connection. Avoid clicking on suspicious links or downloading unsecure files, as that makes them liable to a security breach. It might even be worthwhile to invest in additional cybersecurity software or programs.
7. Ensure Security Controls are Up to Date
Zoom and all video conferencing providers regularly issue updates that address a myriad of features, including security. To ensure that the platform and meetings are secure, all users should regularly check their app to ensure it is running the latest software.
Under settings, there is an option to check for updates. Users simply click that button and Zoom will check their operating system to ensure it’s as current as possible. If it’s not, users can update the app on the same screen, which will help ensure that their meetings are secure going forward.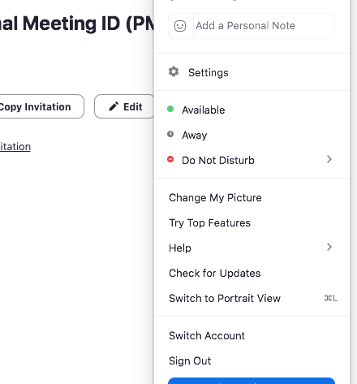
8. Have Backup Platform Options
Zoom is arguably the most widely used video conferencing option being used today, but it’s not the only one. If worse comes to worst and companies don’t feel secure using Zoom or run into periodic issues, they can experiment with other platforms, including:
- Skype
- Google Hangouts
- GoToMeeting
Zoom’s Additional Security Suggestions
Zoom recently announced additional measures they would be taking to protect people’s privacy when using their service. According to the Zoom statement:
Beginning April 18, every paid Zoom customer can opt in or out of a specific data center region. This will determine the meeting servers and Zoom connectors that can be used to connect to Zoom meetings or webinars you are hosting and ensure the best-quality service.
Starting April 18, with respect to data in transit, Zoom admins and account owners of paid accounts can, at the account, group, or user level:
- Opt out of specific data center regions
- Opt into specific data center regions
You will not be able to change or opt out of your default region, which will be locked. The default region is the region where a customer’s account is provisioned. For the majority of our customers, this is the United States.
This feature gives our customers more control over their data and their interaction with our global network when using Zoom’s industry-leading video communication services.
These features will allow users to localize the servers that are being used for their meetings and video conferencing, helping to prevent unwanted interruption from hackers across the globe. Undoubtedly, Zoom will continue to monitor and roll out new security features as new threats arise.
frequently asked questions
Does Zoom offer end-to-end encryption?
Yes, Zoom offers end-to-end encryption (E2EE) for meetings, but it must be enabled rather than assumed to be in use. In a standard Zoom meeting, audio, video and shared content are encrypted in transit, while Zoom’s servers manage the encryption keys. When E2EE is enabled, meeting keys are generated by participants’ devices and Zoom does not have access to those keys. E2EE also disables several features, including cloud recording, live transcription, Zoom AI features and telephone or SIP/H.323 participation. Because E2EE limits some meeting functionality, organizations should determine whether the additional protection is appropriate for a particular meeting.
Are Zoom’s security settings enabled by default?
Zoom includes security protections such as passcodes and Waiting Room options, but default settings can vary by account type and administrator configuration. Zoom has also changed its default security settings over time. For example, Zoom introduced required passcodes and default Waiting Room protections for certain meetings and accounts in 2020, while current account settings allow organizations to require a passcode, Waiting Room or authenticated users as a security option. The host or administrator can also control screen-sharing permissions. Because organizational administrators can change or lock settings, users should review the configuration of their specific Zoom account rather than assume that a particular security setting is enabled.
Is Zoom safe for confidential or regulated information?
Whether Zoom is appropriate for confidential or regulated information depends on the type of information, the organization’s account and the requirements that apply. For example, organizations subject to HIPAA may use Zoom in a HIPAA-compliant program with a Business Associate Agreement and appropriate safeguards. Other regulatory requirements may impose different obligations. Organizations handling sensitive information should use an account and configuration that meet their specific requirements rather than assuming that any Zoom account is appropriate for regulated data.
What are the privacy considerations for AI meeting assistants and transcription?
AI meeting assistants and transcription features introduce additional privacy considerations because they can turn meeting conversations into transcripts, summaries and other persistent data. Organizations should consider who can enable these features, how participants are notified, who can access the resulting information, where it is stored and how long it is retained. Zoom’s Meeting Summary with AI, for example, uses speech-to-text data to generate summaries and can share those summaries with participants after a meeting. E2EE meetings disable Zoom AI features, including Meeting Summary. Organizations should also consider applicable consent, privacy and records-retention requirements when using AI features to process meeting content.
What should you do if someone disrupts a meeting in progress?
If someone disrupts a Zoom meeting, hosts and co-hosts can use several in-meeting controls to respond. Depending on the situation, they can remove a participant, restrict participants’ ability to share their screens, mute participants, lock the meeting to prevent new participants from joining or use **Suspend Participant Activities** to immediately turn off participants’ audio, video and screen-sharing and lock the meeting. These controls can help contain an active disruption while the host determines what further action is needed. Knowing where these controls are before a meeting begins can make it easier to respond quickly.